Key Archival of EFS Recovery Certificate
As of version 7.6, Backup for Windows supports EFS-encrypted file backup and restore: encrypted files are backed up 'as is', i.e. in an encrypted state. To decrypt these files after restoring them to any location other than the original computer, add the Key Recovery Agent for EFS-encrypted files and archive this Agent certificate to a safe place.
Follow these steps:
- Step 1. Add Key Recovery Agent Certificate Template
- Step 2. Request Personal Administrator Certificate
- Step 3. Add a Key Recovery Agent Certificate Using Group Policy
- Step 4. Force Update Group Policies
- Step 5. Use Key Archival
Step 1. Add Key Recovery Agent Certificate Template
Add the Key Recovery Agent certificate template to the list of available certificate templates.
- Log in to the Certification Authority computer with administrative rights.
- In Windows Administrative Tools, click Certification Authority.
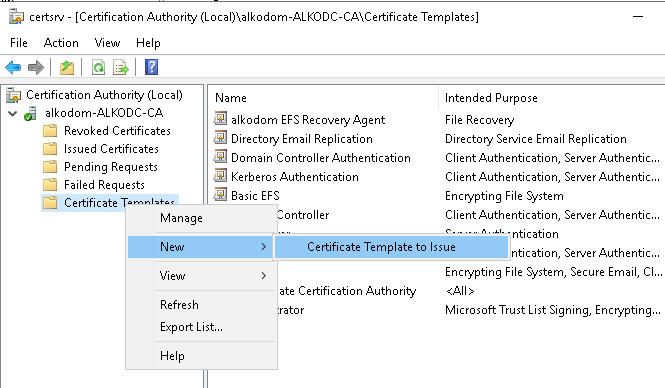
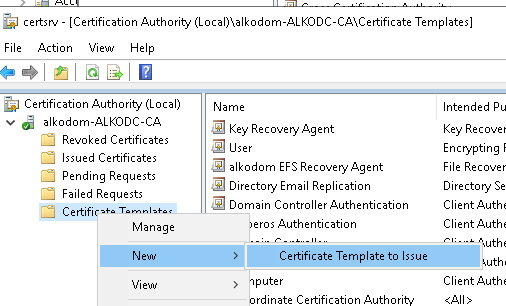
- In Certification Authority, right-click Certificate Templates and select New > Certificate Template to Issue.
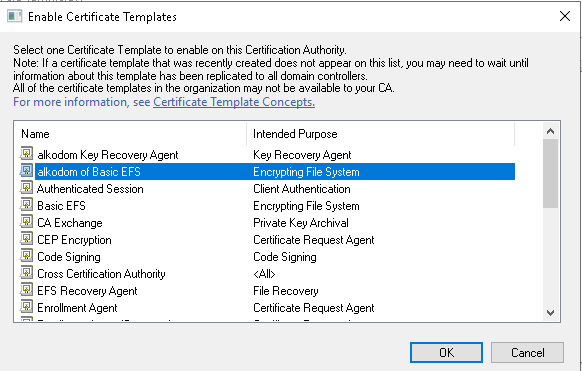
- Select Key Recovery Agent in the list of certificate templates.
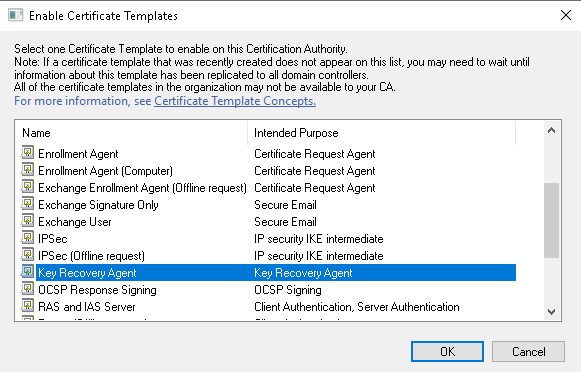
- Click OK to enable this certificate.
- A Key Recovery Agent certificate template appears in the list of Certificate Templates.
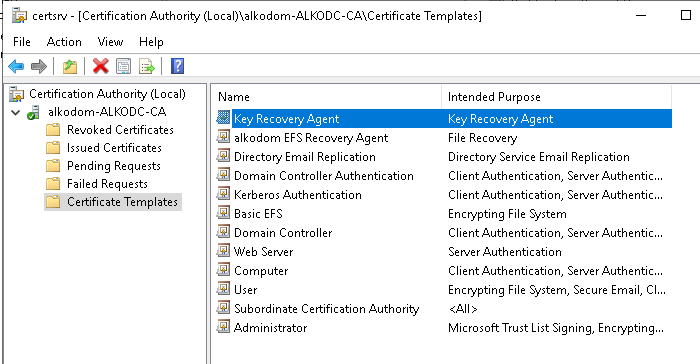
Now you are ready to request a personal administrator certificate using this Key Recovery Agent certificate template.
| Top |
Step 2. Request Personal Administrator Certificate
To request a personal administrator certificate using the Key Recovery Agent template published above, proceed as follows:
- Open the MMC console and add or select the Certificates snap-in.
- Right-click the Certificates folder under the personal store, and select All Tasks > Request New Certificate.
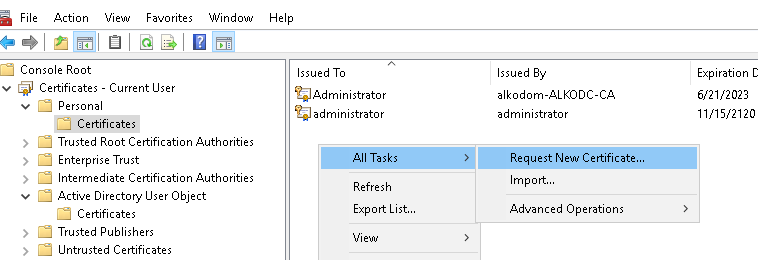
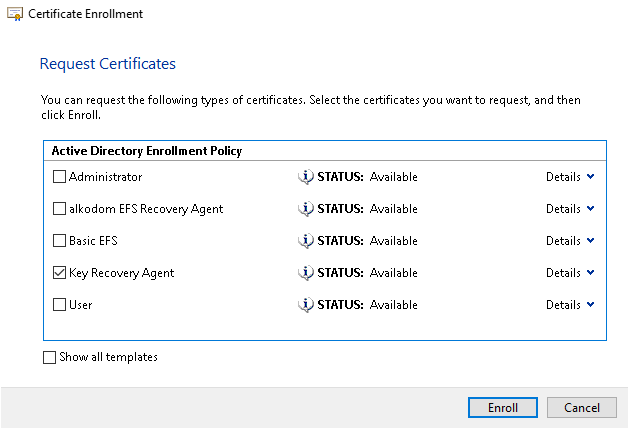
- In the Certificate Enrollment dialog, select Key Recovery Agent in the list of available certificates, then click Enroll.
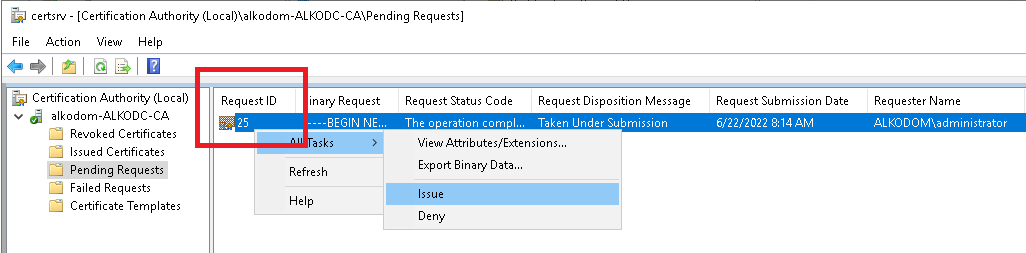
- In Certification Authority, click the Pending Requests folder.
- Right-click your pending request, then select All Tasks > Issue to issue the certificate requested above. Save the Request ID copy of the certificate to a file.
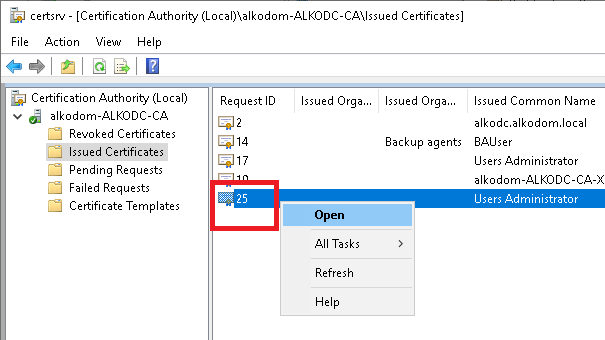
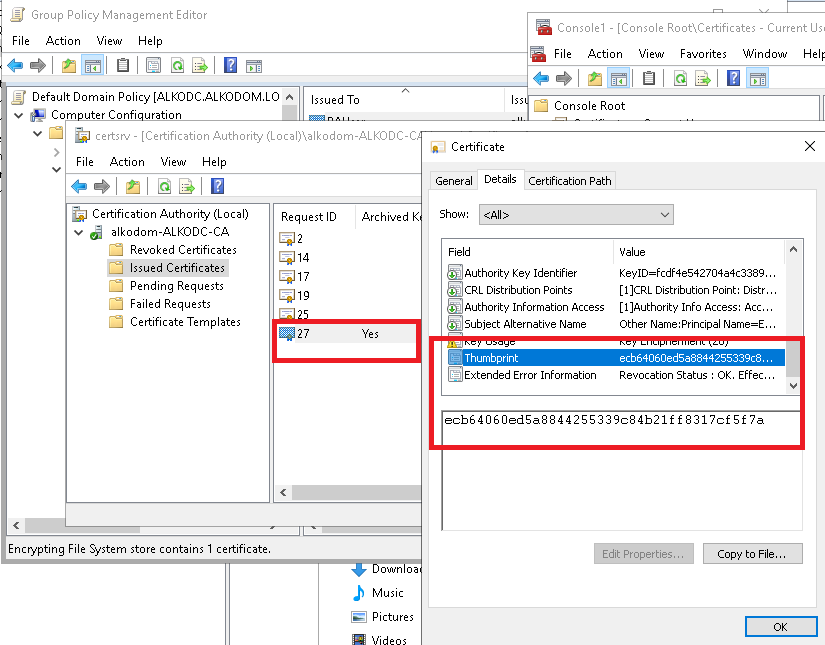
- The certificate appears in the Issued Certificates folder. Right-click the certificate and select Open.
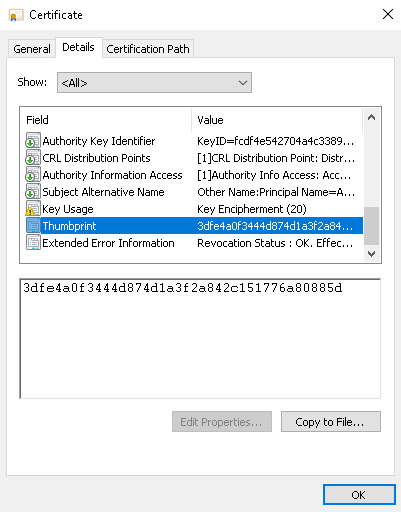
- Select Thumbprint and click Copy to file.
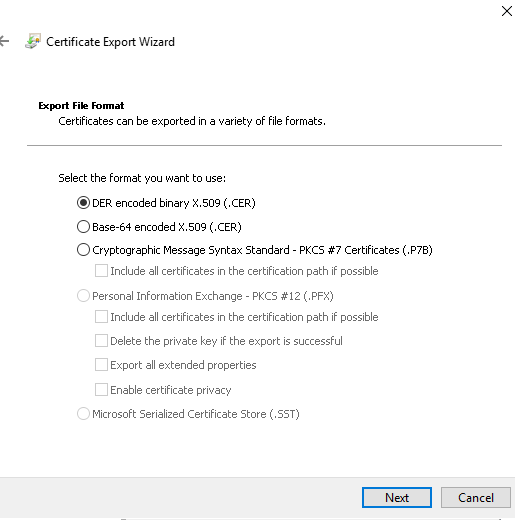
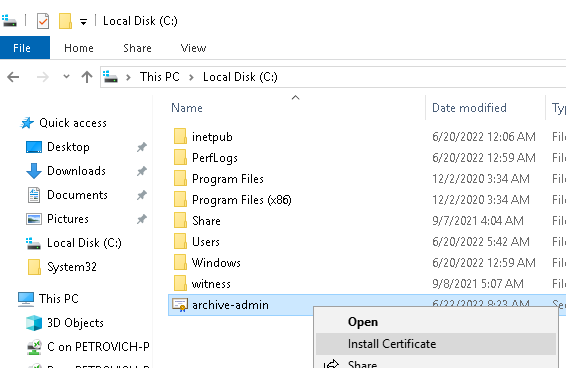
- Export the certificate to a file, for example, archive-admin.cer, with the Certificate Export Wizard. On the Export file format step, select DER encoded binary X.509 (.CER).
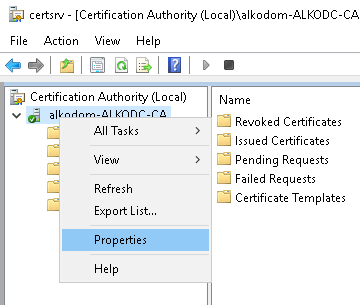
- In the Certification Authority snap-in, add and configure the Recovery Agent. Right-click the domain, then select Properties.
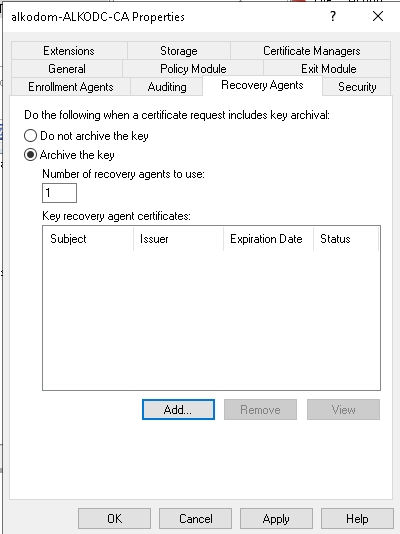
- Click the Recovery Agents tab.
- Select the Archive the Key option. Click Add.
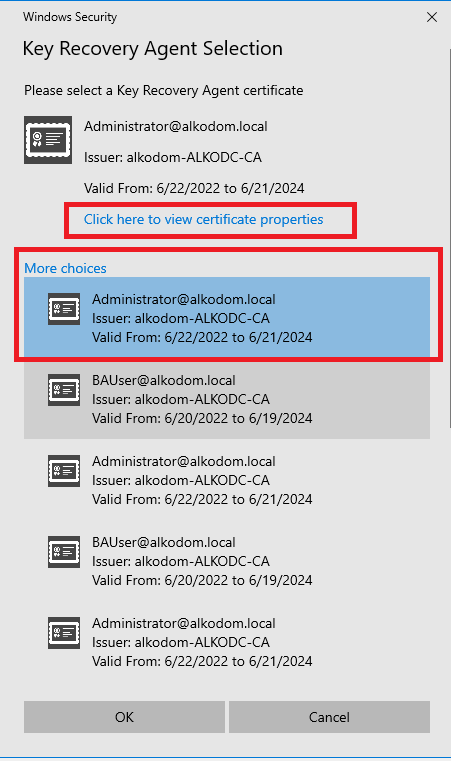
- Select the certificate you issued and verify that the thumbprint of this certificate matches the thumbprint saved to the file above. Click OK.
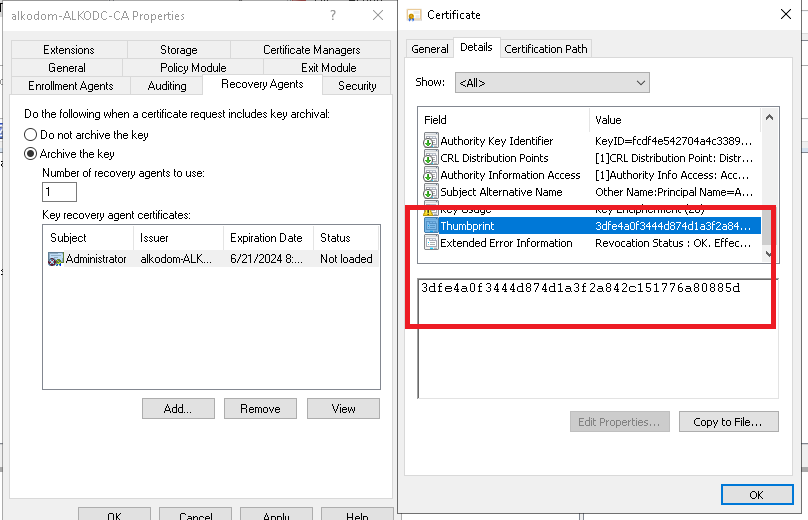
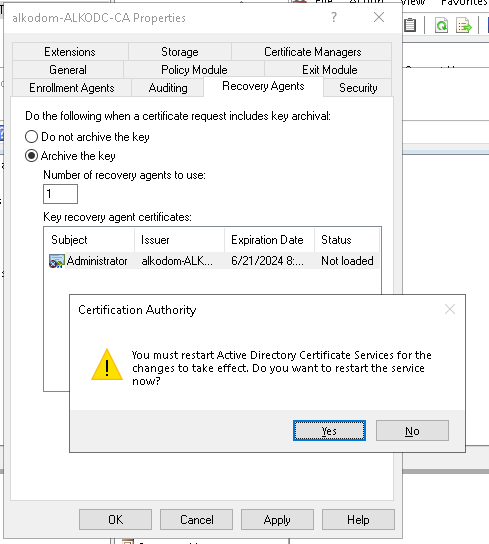
- Restart Active Directory Certificate Services for changes to take effect.
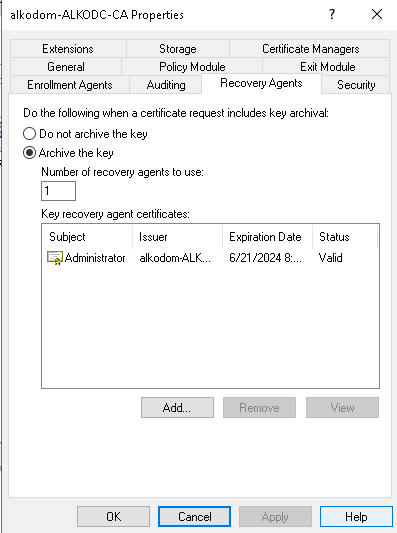
- In Properties, click Recovery Agents to check whether the certificate is valid. Click Cancel.
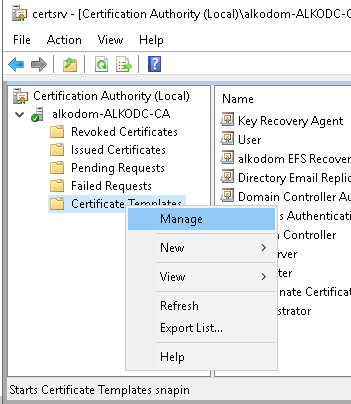
- Add a new EFS template based on the Basic EFS template. In Certification Authority, right-click Certificate Templates and select Manage.
- Right-click the Basic EFS template and select Duplicate Template.
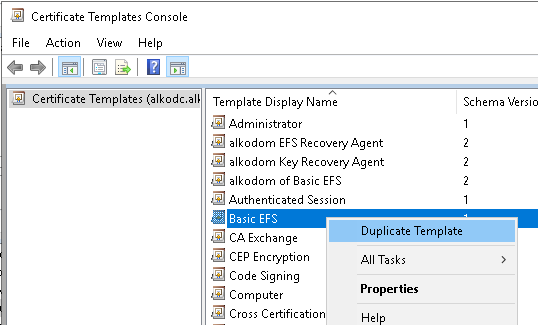
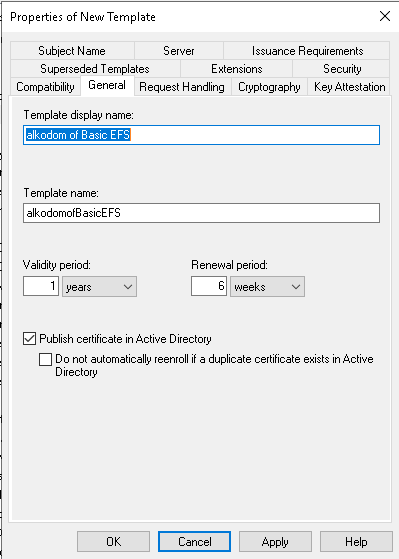
- Configure the new template properties:
- Name the template on the General tab.
* On the Request Handling tab, select **Archive subject's encryption private key**.
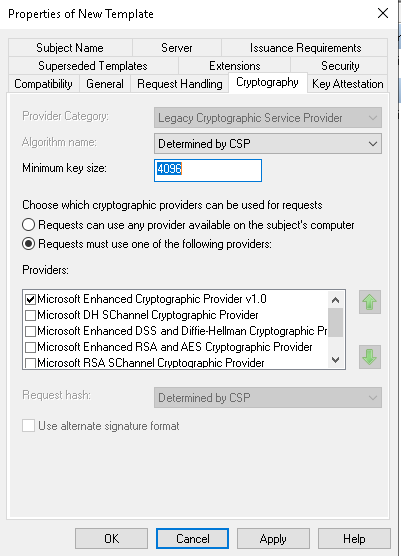
* On the Cryptography tab, set the minimum key size.
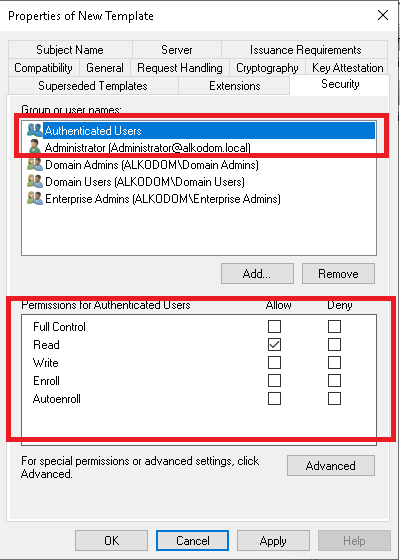
* On the Security tab, grant the Read permission to the Key Recovery Agent account.
- Click Apply.
- Publish the created certificate template. In Certification Authority, right-click Certificate Templates and select New > Certificate Template to Issue.
- Select your template by name and click OK to enable it.
Now you are ready to add this Key Recovery Agent to Group Policy. | Top |
Step 3. Add a Key Recovery Agent Certificate Using Group Policy
- Open the Group Policy Management snap-in.
- Right-click Default Domain Policy and select Link Enabled.
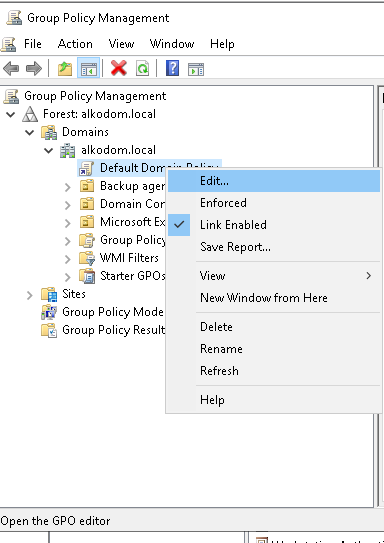
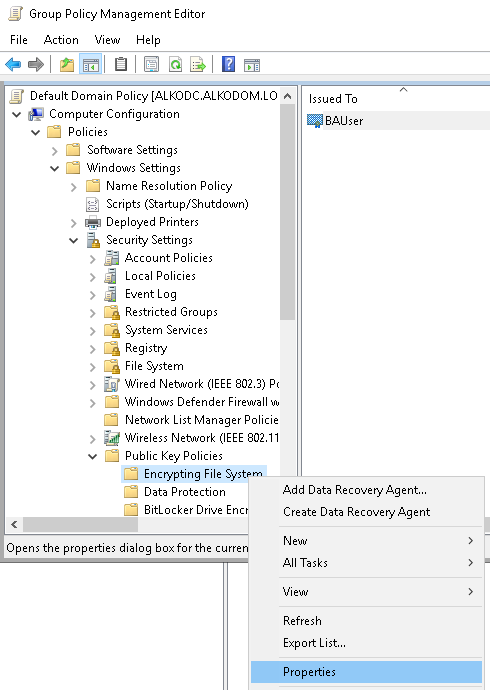
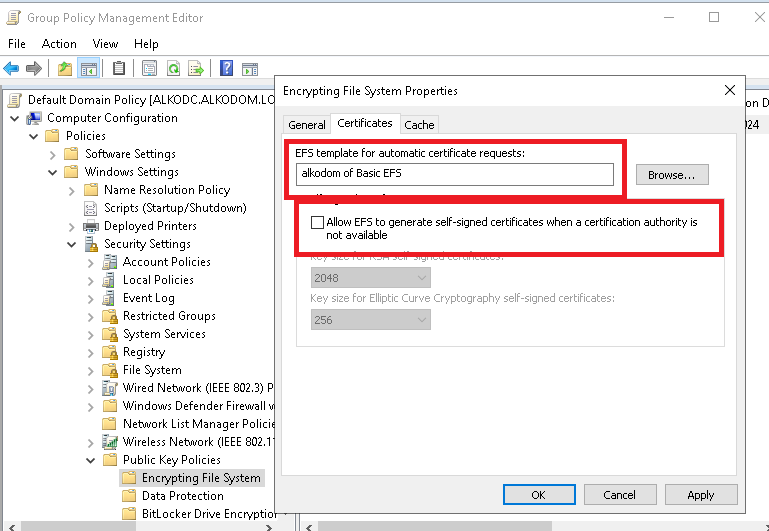
- To edit the Default Domain policy, expand Computer Configuration > Policies > Windows Settings > Security Settings > Public Key Policies. Right-click Encrypting File System and select Properties.
- On the General tab for Encrypting File System (EFS), select Allow.
- On the Certificates tab, select your template as the EFS template for automatic certificate requests and clear the Allow EFS to generate self-signed certificates when a certification authority is not available check box.
- Click Apply.
Now you are ready to update group policies on the computers where you want to back up EFS files.
| Top |
Step 4. Force Update Group Policies
- Log in to the original client computer and run gpupdate /force.
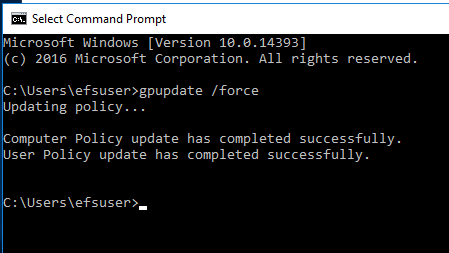
Now the created Group Policy is used on this computer. You are ready to check whether key archival works properly.
| Top |
Step 5. Use Key Archival
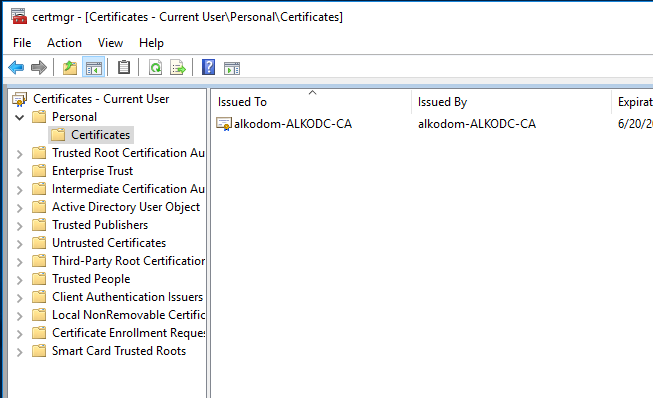
- Log in to the original computer as a standard user that does not have an EFS certificate.
- Create and encrypt a file.
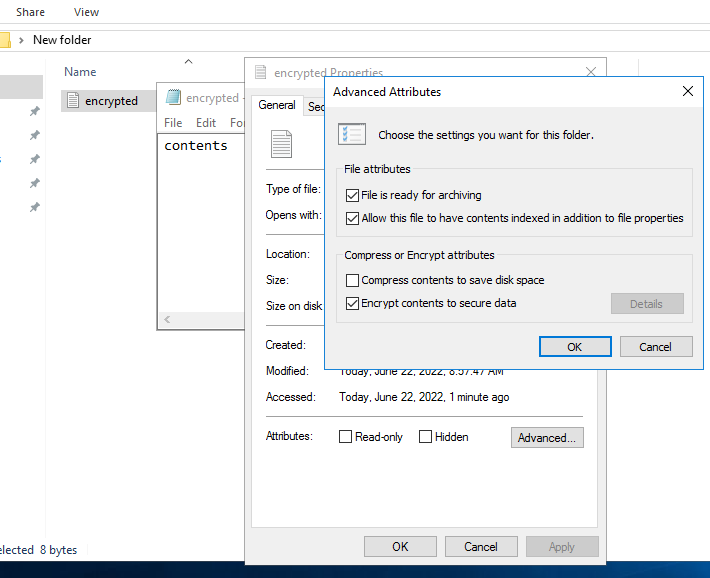
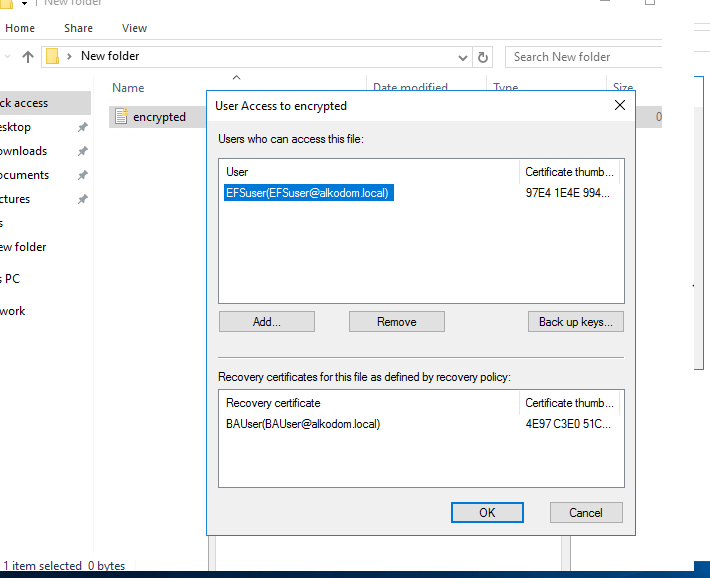
- Make sure that the new user has access to the encrypted file.
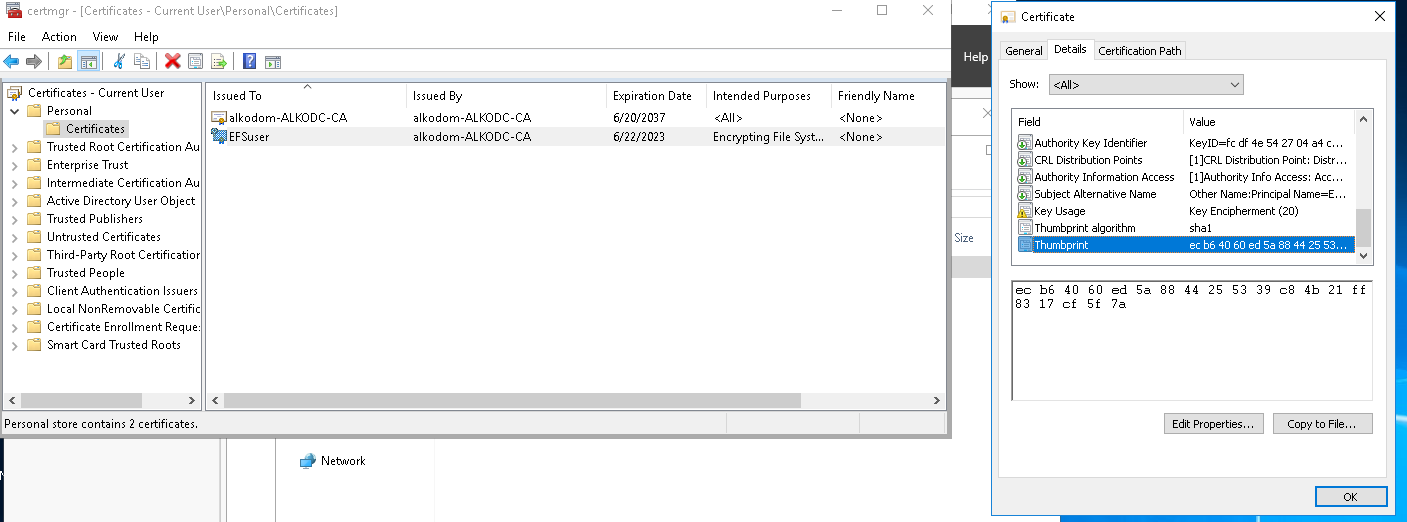
- The same certificate appears in the user's personal store.
- Log in to the Certification Authority computer.
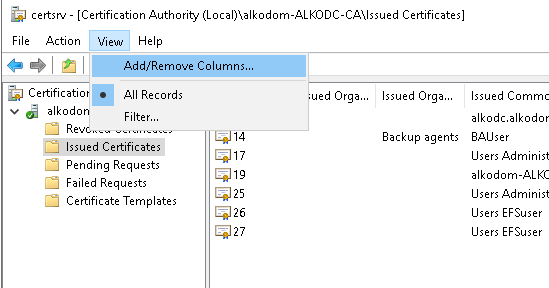
- In the Certification Authority snap-in, click View > Add/Remove Columns....
- Add the Archived Key column and move it to the top of the list. Click OK.
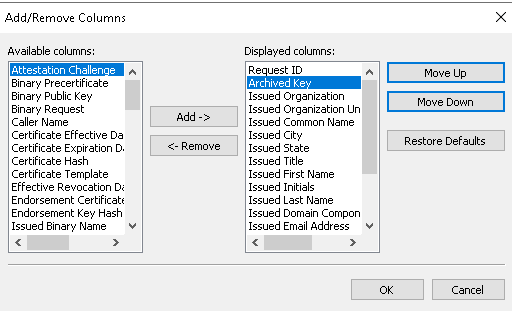
- Note that a standard user certificate was automatically issued and archived.
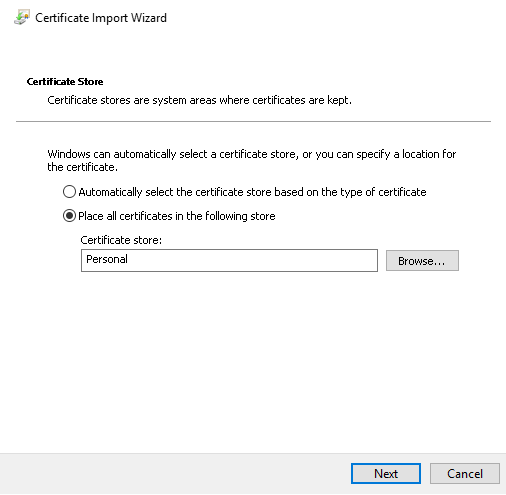
- Install previously exported Recovery Agent certificate c:\archive-admin.cer to the administrator's personal store on the Certification Authority computer.
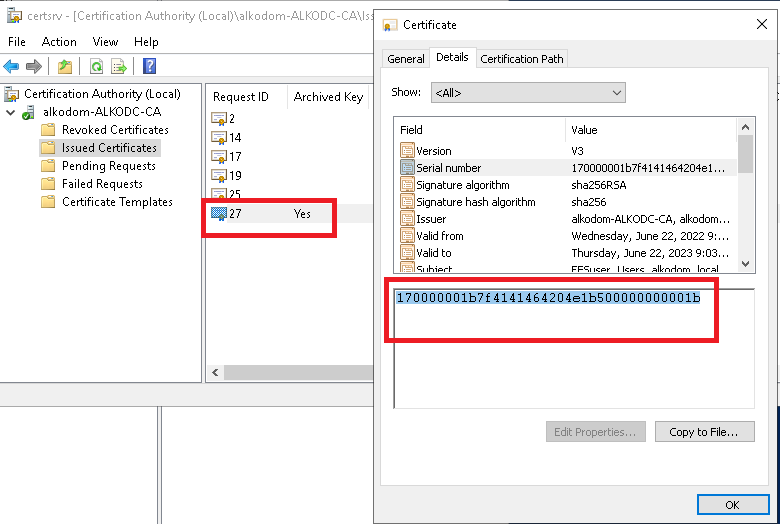
- Locate the issued and archived ordinary user EFS certificate in Certification Authority and copy the serial number to the clipboard.
- Run PowerShell as Administrator.
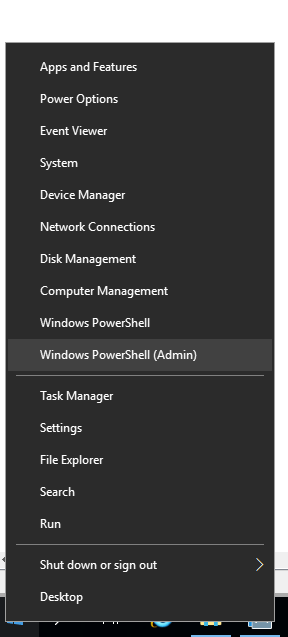
- Execute the following commands in the PowerShell window. At the last step, specify the recovered .pfx password.
 cd /

mkdir keyrecoverdir

cd .\keyrecoverdir\

certutil -getkey 170000001b7f4141464204e1b500000000001b rawkeyinfo

certutil -recoverkey .\rawkeyinfo recovered.pfx
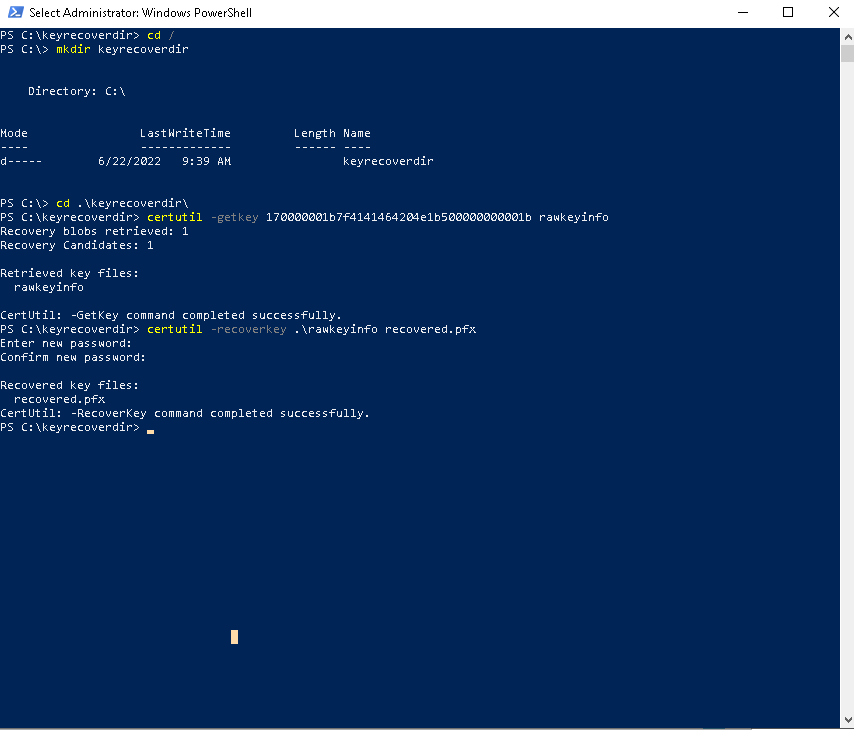
- Now the standard user .pfx certificate is recovered.
- Log in to the original client computer where you created the EFS-encrypted file.
- Delete the EFS keys/certificate.
- Place recovered.pfx in the file system.
- Install recovered.pfx to the ordinary user's personal certificate store.
- Log in again to the original client computer to uncache the certificate thumbprint.
- Try to open your EFS-encrypted file to make sure everything is fine.
| Top |