Encryption and Unattended Access
MSP360 Connect sends all the data over an HTTPS channel (which means the data is secure from being stolen).
However, you can enable additional encryption on the remote host side, with the encryption key known only to you. While regular sessions require only Computer ID and PIN, encrypted sessions also require an encryption key that has to be transferred from the remote host to the client side via another communication channel.
The app uses the RSA algorithm to encrypt sessions. Encryption can be enabled in the app's settings on the remote host computer:
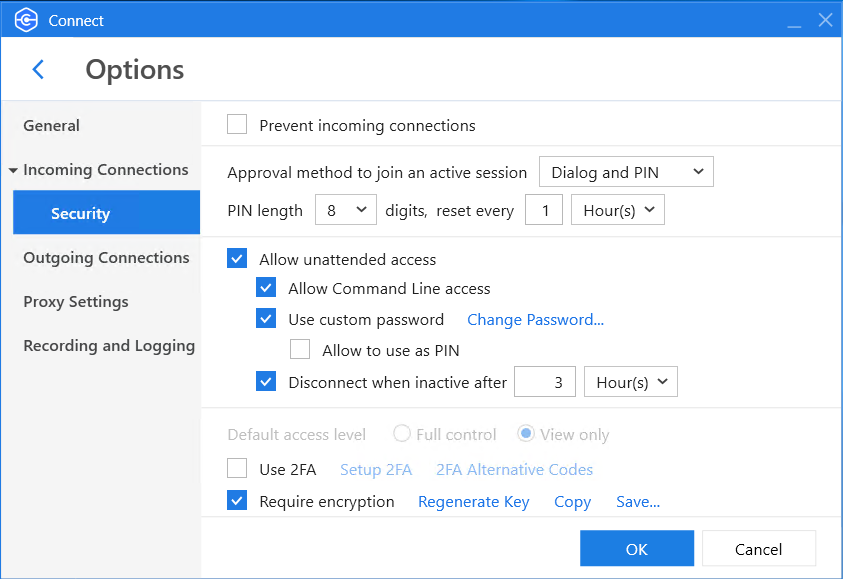
Once enabled, the remote host should provide you with that encryption key. You, in turn, should specify the encryption key in the connection settings.
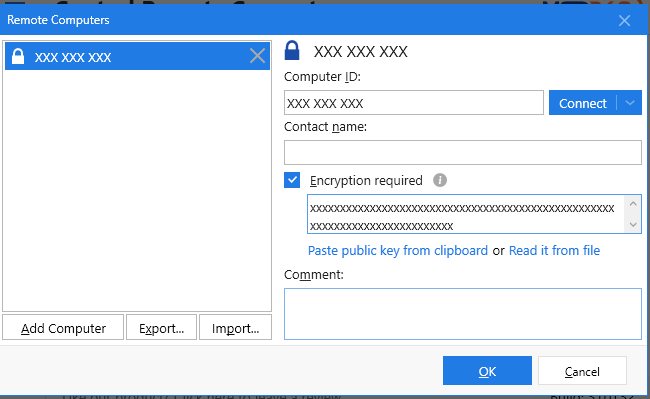
The encryption key has to be specified only once, and it will always be used when establishing a connection. The encryption key is never changed unless it is manually regenerated on the remote host in the app's settings. A regenerated encryption key has to be provided again to all users who want to connect to the remote host computer.
Click Regenerate Key to change the key if you suspect that it has been compromised. You can copy or save it.
Using encryption ensures that no transferred data is interpretable in the event of data interception.